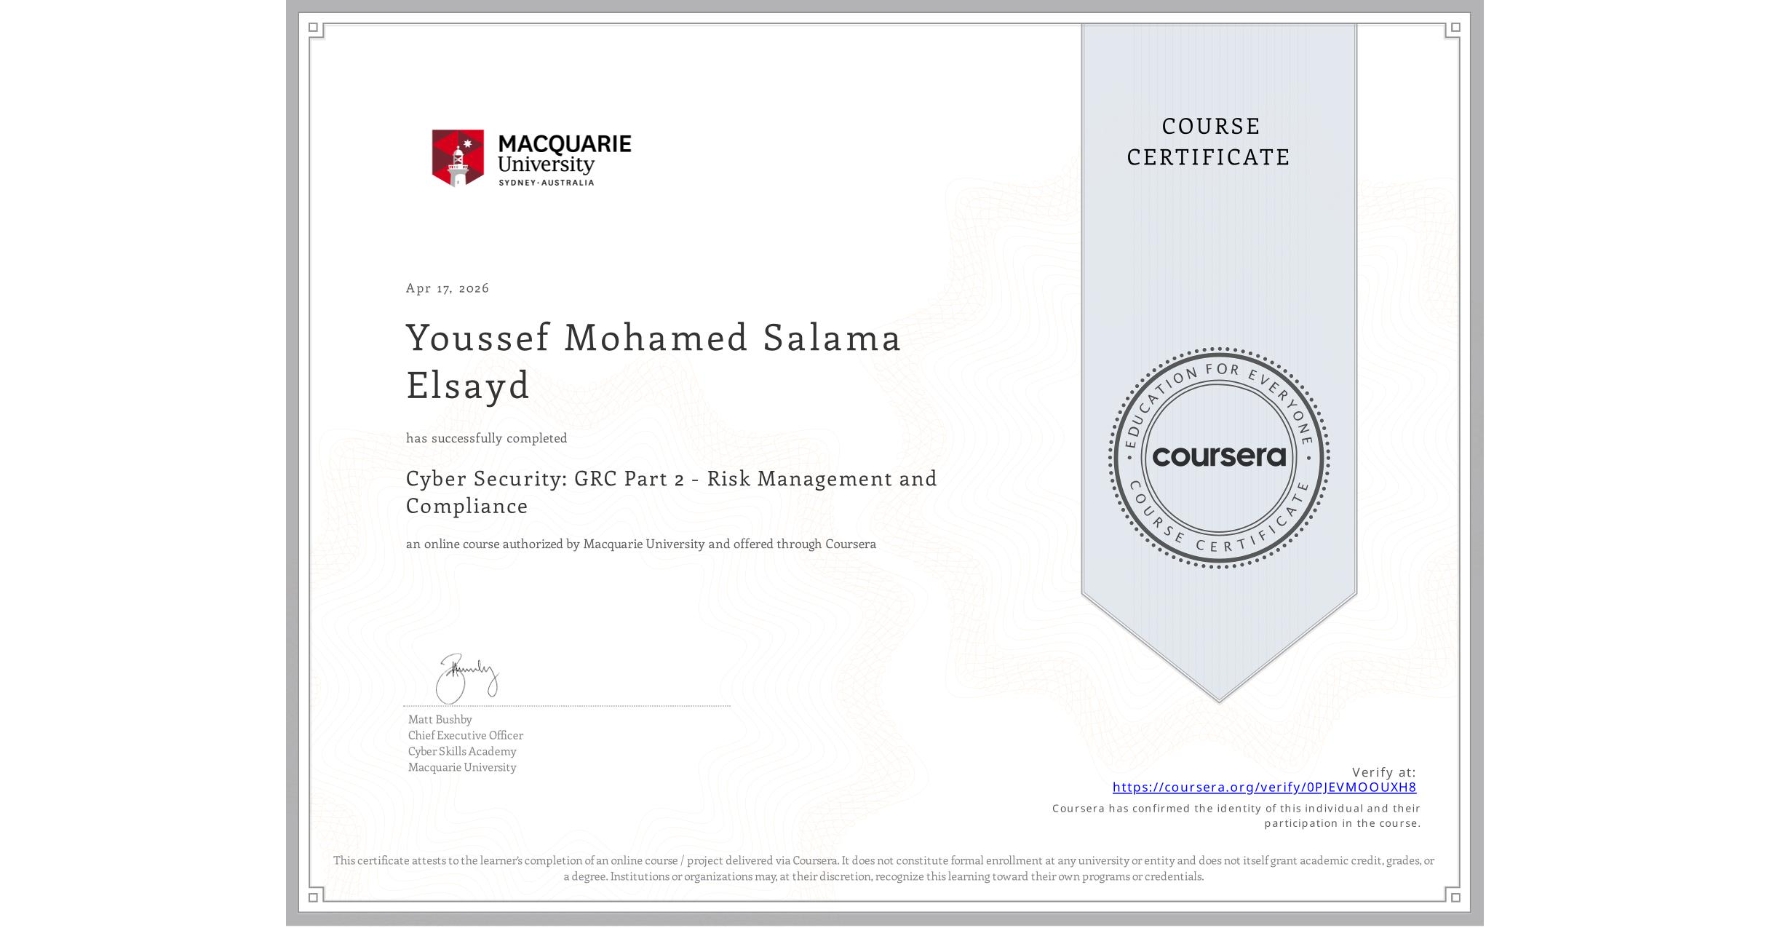
Cyber Security: GRC Part 2 - Risk Management and Compliance
Completed by Youssef Mohamed Salama Elsayd
April 17, 2026
12 hours (approximately)
Youssef Mohamed Salama Elsayd 's account is verified. Coursera certifies their successful completion of Cyber Security: GRC Part 2 - Risk Management and Compliance

What you will learn
Design and implement effective governance models, including risk management structures and the Three Lines of Defence.
Craft a cyber security strategy aligned to business goals, integrating established frameworks including NIST, CIS, and ISO 27001.
Assess and quantify organisational cyber risks using both qualitative and quantitative methodologies.
Lead high-stakes decision-making during real-time cyber incidents, drawing on playbooks and threat intelligence.
Skills you will gain
- Category: Risk Mitigation
- Category: Threat Management
- Category: Business Risk Management
- Category: Cyber Risk
- Category: Cyber Security Policies
- Category: Cyber Security Strategy
- Category: Governance Risk Management and Compliance
- Category: Security Strategy
- Category: Risk Management
- Category: Crisis Management
- Category: Risk Analysis
- Category: Security Management